开源贡献日报 · 2026-10-16
开源贡献日报 · 2026-10-16
开源贡献日报 2026-10-16 封面
记录可验证的修复进展,也记录仍有空间参与的架构与规范讨论。
数据截止:2026-10-16T23:48:16+08:00(Asia/Singapore)。以下是当日截至该时间的记录。
公开资料覆盖:不完整;截至 2026-10-16 23:48 SGT。保留当日有公开技术结果的修复、测试、review响应、提交与合并;PR及讨论覆盖不完整。
1 今天跟进与完成的结果
- OpenCode configured model limits (
anomalyco/opencode#55768,pr) — Merged on 16 October after 37 focused tests and the repository check passed.;Seeded configured limits before model transforms while preserving final config override precedence. - Cindy native Linux RPM packages (
makecindy/cindy#3666,pr) — Review correction pushed; 45 targeted tests and syntax/diff checks passed. Current-head CI and native QA remain pending.;Kept the personal Linux build DEB-only while preserving default dual-format packaging. - Multica per-agent execution directory mode (
multica-ai/multica#9278,pr) — PR submitted; focused runtime, path mutex and lock checks passed.;Added per-agent none, in-place and worktree modes with project-default inheritance. - Multica GitHub App permission refresh (
multica-ai/multica#9279,issue) — A community reproduction confirmed the permission gap; hosted App access is still required for end-to-end validation.;Explained the permission and installation refresh sequence needed before snapshot and wakeup validation. - Pi top-level effort bounds (
earendil-works/pi#10063,issue) — Fork fix and bounded regression test shared; 16 targeted tests and npm run check passed.;Covered low and medium top-level effort limits and documented validation boundaries. - Cindy mobile device discovery review follow-up (
makecindy/cindy#4358,pr) — Both review threads were confirmed resolved at the unchanged head; existing checks were green.;Answered and resolved the remaining review thread; no code change or test rerun was needed. - Cherry sparse response lifecycle (
CherryHQ/cherry-studio#20282,pr) — Conflict repair passed 24 focused tests plus ESLint and patch checks.;Rebased the sparse response lifecycle fix on the current base. - Cherry OpenRouter session routing (
CherryHQ/cherry-studio#20432,pr) — Conflict repair passed 274 focused tests, Node typecheck, formatting and lint.;Restored a clean reviewable diff for the session routing change. - Cherry knowledge-base routes (
CherryHQ/cherry-studio#20743,pr) — Conflict repair passed 294 tests (12 skipped) and focused native checks; full affected check remains incomplete.;Updated the route fix against the current base and retained the validation gap. - Cherry HTTP 400 empty assistant message (
CherryHQ/cherry-studio#19824,pr) — Official transport tests passed 16/16 and native web typecheck passed; no original Windows diagnostic-bundle reproduction is claimed.;Improved visibility of the bounded transport error path. - Cindy Android R8 ONNX consumer rule (
makecindy/cindy#6190,pr) — Draft PR submitted with 45 targeted tests passing; native-device QA and mobile typecheck remain incomplete.;Added a shrinker keep rule for the ONNX runtime JNI consumer. - Pi permission snapshot lifecycle (
earendil-works/pi#11006,issue) — Fork fixed diff posted; 57 focused tests and npm run check passed.;Added regression coverage for permission snapshot refresh after access changes. - Pi static and OAuth-backed model catalog (
earendil-works/pi#11021,issue) — Fork fixed diff posted; 21 focused tests and npm run check passed. An earlier full-suite run was non-final and did not pass at the final head.;Preserved the static catalog baseline while adding account-scoped OAuth catalog refresh. - Cherry PR #21212 web typecheck (
CherryHQ/cherry-studio#21206,pr) — Exact-head Type checks and Verify planned checks passed; maintainer review remains pending.;Closed the previously incomplete web typecheck gap with remote CI evidence. - OpenCode shortcut composer reference (
anomalyco/opencode#56065,issue) — Fixed fork reference passed 39 composer tests and canonical check/lint 35/35; Windows keeper run is queued and Electron UI is not yet verified.;Shared a fixed reference implementation and kept the platform validation limitation explicit. Cindy native bridge unknown image input (
makecindy/cindy#6026,pr) — Merged on 16 October; linked issue #6023 status was not verified.;The change preserves unknown image input through native provider bridges.- 今日合并:已核实至少 4。
- 今日关闭(未合并):已核实至少 0。
今天合并的旧 PR
旧 PR 指今天之前创建、今天合并的 PR;已包含在今日合并总数中。
| PR | 创建日期 | 合并时间 |
|---|---|---|
| fix(ai): preserve GLM-5.2 thinking on Ollama Cloud | 2026-10-05 | 2026-10-16 03:39:37 |
| fix(mobile): avoid stale device roster snapshot | 2026-09-12 | 2026-10-16 10:57:56 |
| fix(providers): preserve unknown image input in native bridges | 2026-10-14 | 2026-10-16 23:07:16 |
时间均为 Asia/Singapore。
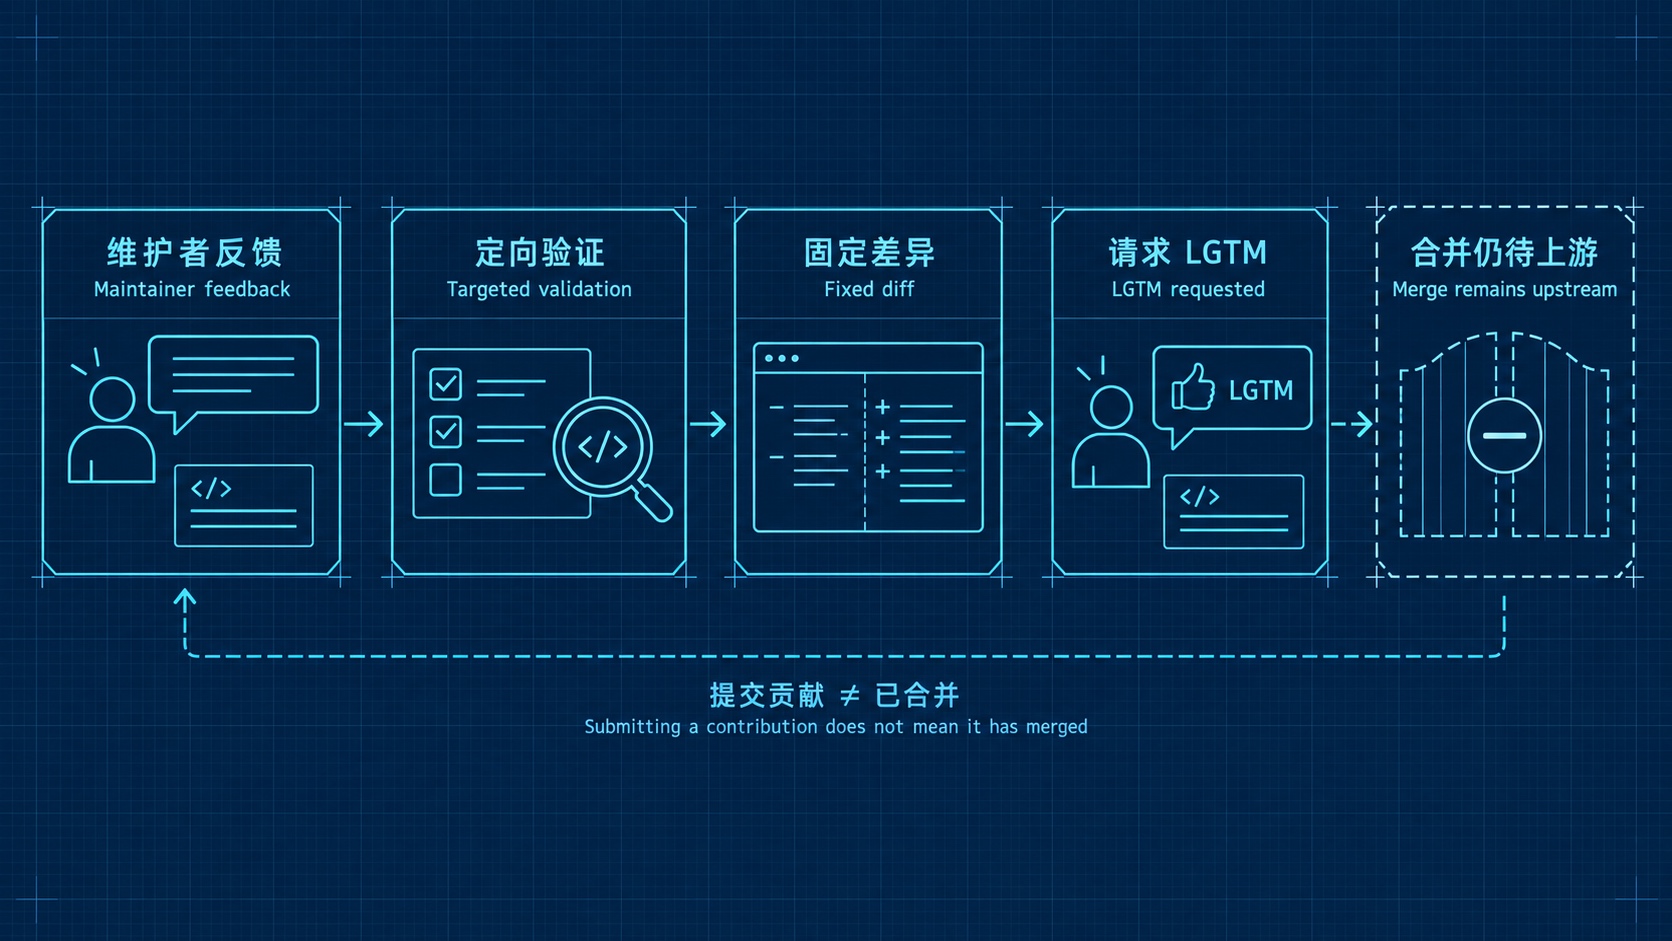
从维护者反馈到定向验证、固定差异与上游合并门槛的流程图
2 今天吸取的经验
- A cleanup path must not replace the original failure cause; regression coverage should verify the priority of the preserved error.
- 证据:GitHub
- A platform comparison only supports the exact operating-system and tool versions tested. When the reporter environment is unavailable, narrow the claim and preserve that validation gap.
- 证据:GitHub
- Declare native build dependencies in CI images instead of relying on incidental preinstalled packages; verify the resulting package on each target architecture.
- 证据:GitHub
- Focused regression checks can validate a catalog or cache boundary while broader acceptance is still pending; keep the static baseline and state the authenticated-refresh limitation separately.
- 证据:GitHub
3 有意思的模块与行业动态
- Static model catalog and OAuth account catalogs(
earendil-works/pi)- 讨论问题:This case examines how a stable static model list should coexist with an OAuth-backed account catalog, including when authenticated refresh populates the account-scoped cache.
- 行业动态:From this case, optional account discovery should enrich a usable local baseline without making first-run model discovery depend on a successful authenticated refresh.
- 总结点:Keep a predictable static baseline before an account cache is populated.;Scope cached account catalog data to the account and endpoint, and make refresh limits explicit.
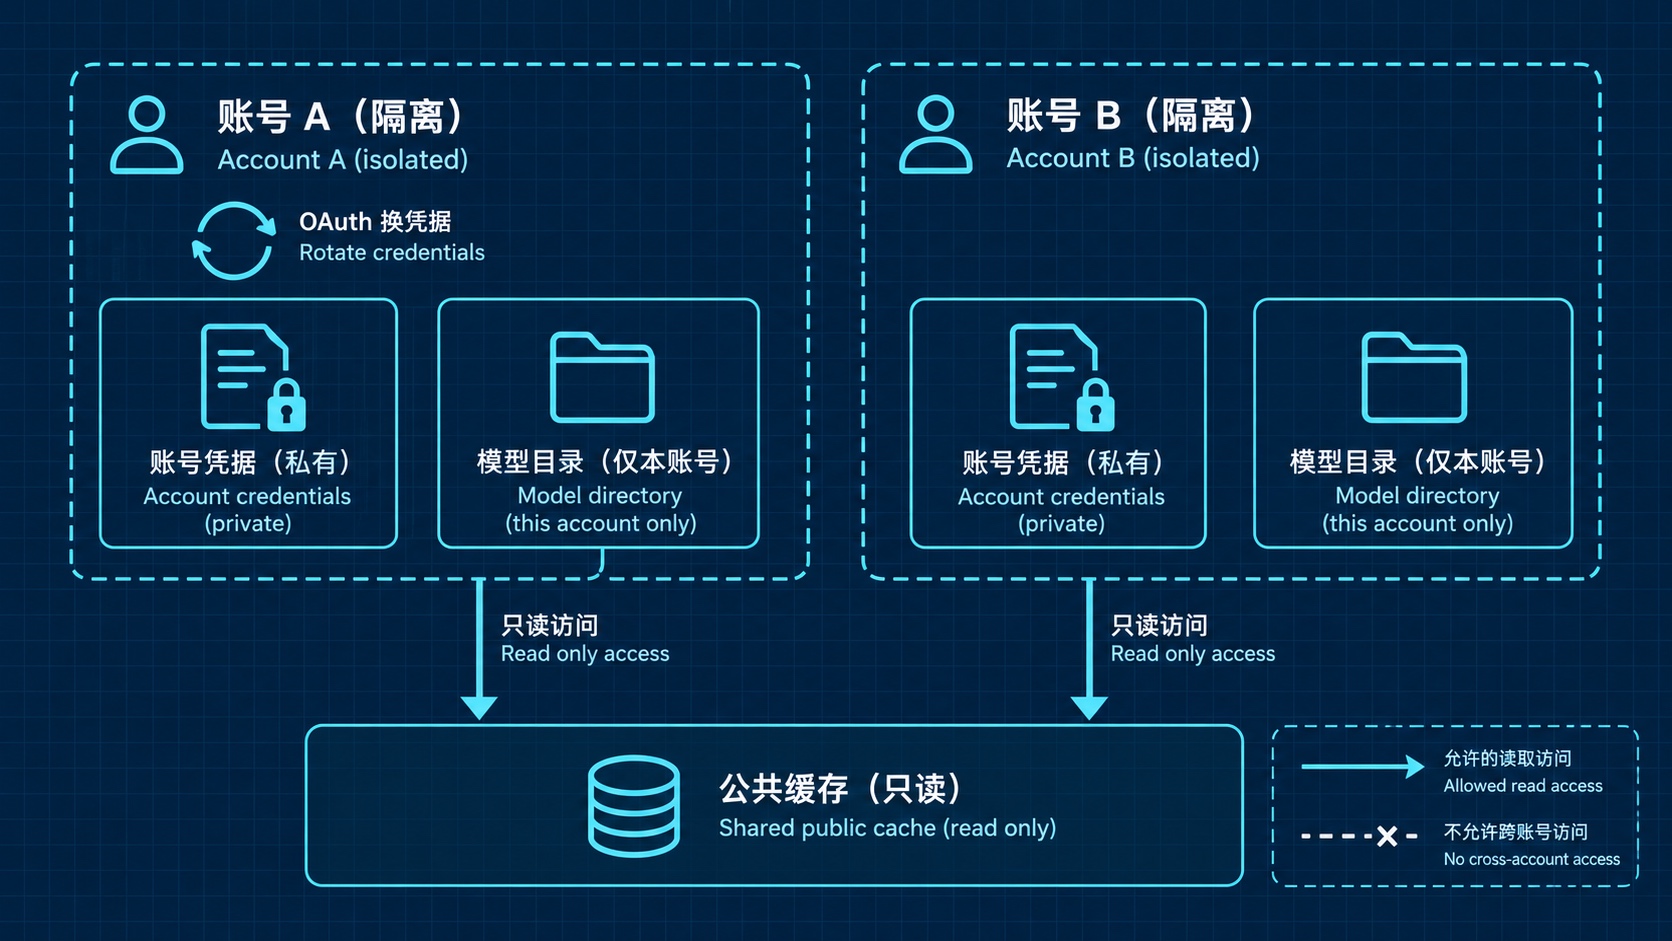
账号凭据、模型目录与公共缓存的隔离关系
- Permission snapshot refresh lifecycle(
earendil-works/pi)- 讨论问题:This case explores when a permission snapshot should refresh after the authorization or installation state changes.
- 行业动态:From this case, systems that cache permission snapshots need a visible refresh boundary when external access changes.
- 总结点:Separate permission changes from snapshot refresh.;Test both stale-snapshot and refreshed-access paths.
4 今天在哪些项目做了贡献
anomalyco/opencode:Merged configured model limit seeding with precedence preserved; delivered a shortcut-composer reference fix with focused checks while Windows UI validation remains queued.(来源 1、来源 2)makecindy/cindy:Revised Linux packaging after review, resolved a mobile device discovery review thread, submitted an Android R8/ONNX keep-rule draft, and merged a native-bridge fix preserving unknown image input.(来源 1、来源 2、来源 3、来源 4)multica-ai/multica:Submitted per-agent execution-directory support and documented the GitHub App permission refresh sequence from a community reproduction.(来源 1、来源 2)earendil-works/pi:Shared three bounded reference fixes with focused regression checks, including account-scoped catalog refresh and permission snapshot lifecycle cases.(来源 1、来源 2、来源 3)CherryHQ/cherry-studio:Delivered conflict repairs and focused validation across several existing PRs; remote exact-head checks now also close the #21212 web typecheck gap.(来源 1、来源 2、来源 3、来源 4、来源 5)